Software agency in Breda, NL · AI · data · Kotlin & Java
AI solutions on your own data, hosted securely in the EU.
Mardi Gras Developers is a software team of two senior engineers from Breda, the Netherlands. We build AI solutions and private AI platforms, and what lies underneath them: secure infrastructure, data migrations and backends in Kotlin and Java. You work directly with the engineers who build it.
You speak to Kevin or Pascal directly. The intro call takes 30 minutes.
private-ai / request-flowlive
A private AI platform for a financial services firm. Read the case
In numbers
35,000
active users of our apps in the 2026 season
7
apps live from one codebase
6
admin portals in production
10+ years
of Java, Kotlin and cloud experience
In production at, among othersKielegat · Kruikenstad · Oeteldonk · Boemeldonck · Moesland · Carnaval in Uje · Carnavalsmaatje
Security
AI security: four measures in every system
An AI model makes no hard distinction between instructions and data, and an agent acts on its own. That is why OWASP ranks prompt injection as the number one risk for AI applications. We build in these four measures by default.
An agent gets only the permissions for its task. What it may not do, an attacker cannot make it do either.
02
A human approves risky actions
Merging, deploying and deleting only happen after a human approves.
03
External content is data
Web pages, emails and documents count as untrusted and stay separated from the user's instruction.
04
Every action recorded
An audit log shows who or what made a change, so you can reconstruct afterwards what happened.
Pick an attack and see where it stops
Five attacks that happen every day, and the layer that stops each one.
Attacker
Zero Trustidentity first, then access
Inputexternal content is data
Permissionsonly what the task needs
Approvala human decides
Your systems
Stopped: Zero TrustAs soon as a flaw in widely used software becomes public, bots scan the whole internet within hours for servers that still have it. With Cloudflare Zero Trust the server opens an outbound tunnel itself and no port is open; a request without a valid identity never reaches the application, even when it has not been patched yet. Patching is still needed, but it buys you time.
Stopped: Zero TrustPasswords leak through phishing and reuse. Behind Zero Trust a password alone is not enough: sign-in goes through your identity provider with a second factor, per application, and access can be revoked at once when someone leaves.
Stopped: InputAn attacker hides a command in a PDF or email that an employee asks the AI to summarise. Because external content stays separated from the instruction, the text is summarised and not carried out. This layer is not watertight, which is why two more follow.
Stopped: PermissionsSuppose an injection does succeed and the agent is told to look up passwords or keys. The agent only has permissions for its task and cannot reach them.
Stopped: ApprovalAn agent, manipulated or simply wrong, prepares an irreversible action. It is only carried out after a human has looked at it and approved it.
Scanner hunts a known vulnerability
Stopped: Zero Trust. As soon as a flaw in widely used software becomes public, bots scan the whole internet within hours for servers that still have it. With Cloudflare Zero Trust the server opens an outbound tunnel itself and no port is open; a request without a valid identity never reaches the application, even when it has not been patched yet. Patching is still needed, but it buys you time.
Stolen password
Stopped: Zero Trust. Passwords leak through phishing and reuse. Behind Zero Trust a password alone is not enough: sign-in goes through your identity provider with a second factor, per application, and access can be revoked at once when someone leaves.
Hidden instruction in a document
Stopped: Input. An attacker hides a command in a PDF or email that an employee asks the AI to summarise. Because external content stays separated from the instruction, the text is summarised and not carried out. This layer is not watertight, which is why two more follow.
Manipulated agent looks for secrets
Stopped: Permissions. Suppose an injection does succeed and the agent is told to look up passwords or keys. The agent only has permissions for its task and cannot reach them.
Agent wants to deploy or delete something
Stopped: Approval. An agent, manipulated or simply wrong, prepares an irreversible action. It is only carried out after a human has looked at it and approved it.
Every step is in the audit log, including the blocked ones.
Services
Seven services around AI, data and backends
Each service has its own page with what you get, how we work and where we have done it before.
A financial services firm wanted its staff to work with AI, without customer data leaving Europe and without depending on a single provider. We built its own AI platform with a model gateway, EU routing that blocks when it cannot be guaranteed, and a masked copy of production data that AI can answer questions about.
We built our own environment in which AI agents prepare software changes across seven repositories. An agent creates an isolated working copy, makes the change, runs the checks and offers the result as a pull request with a live preview. Merging and deploying only happen after a human approves.
Carnavalsmaatje makes sure that people who cannot go to carnival on their own, such as elderly people and people with a disability, can still take part with a volunteer buddy. We built the web application in which participants and buddies register, are matched and receive their tickets.
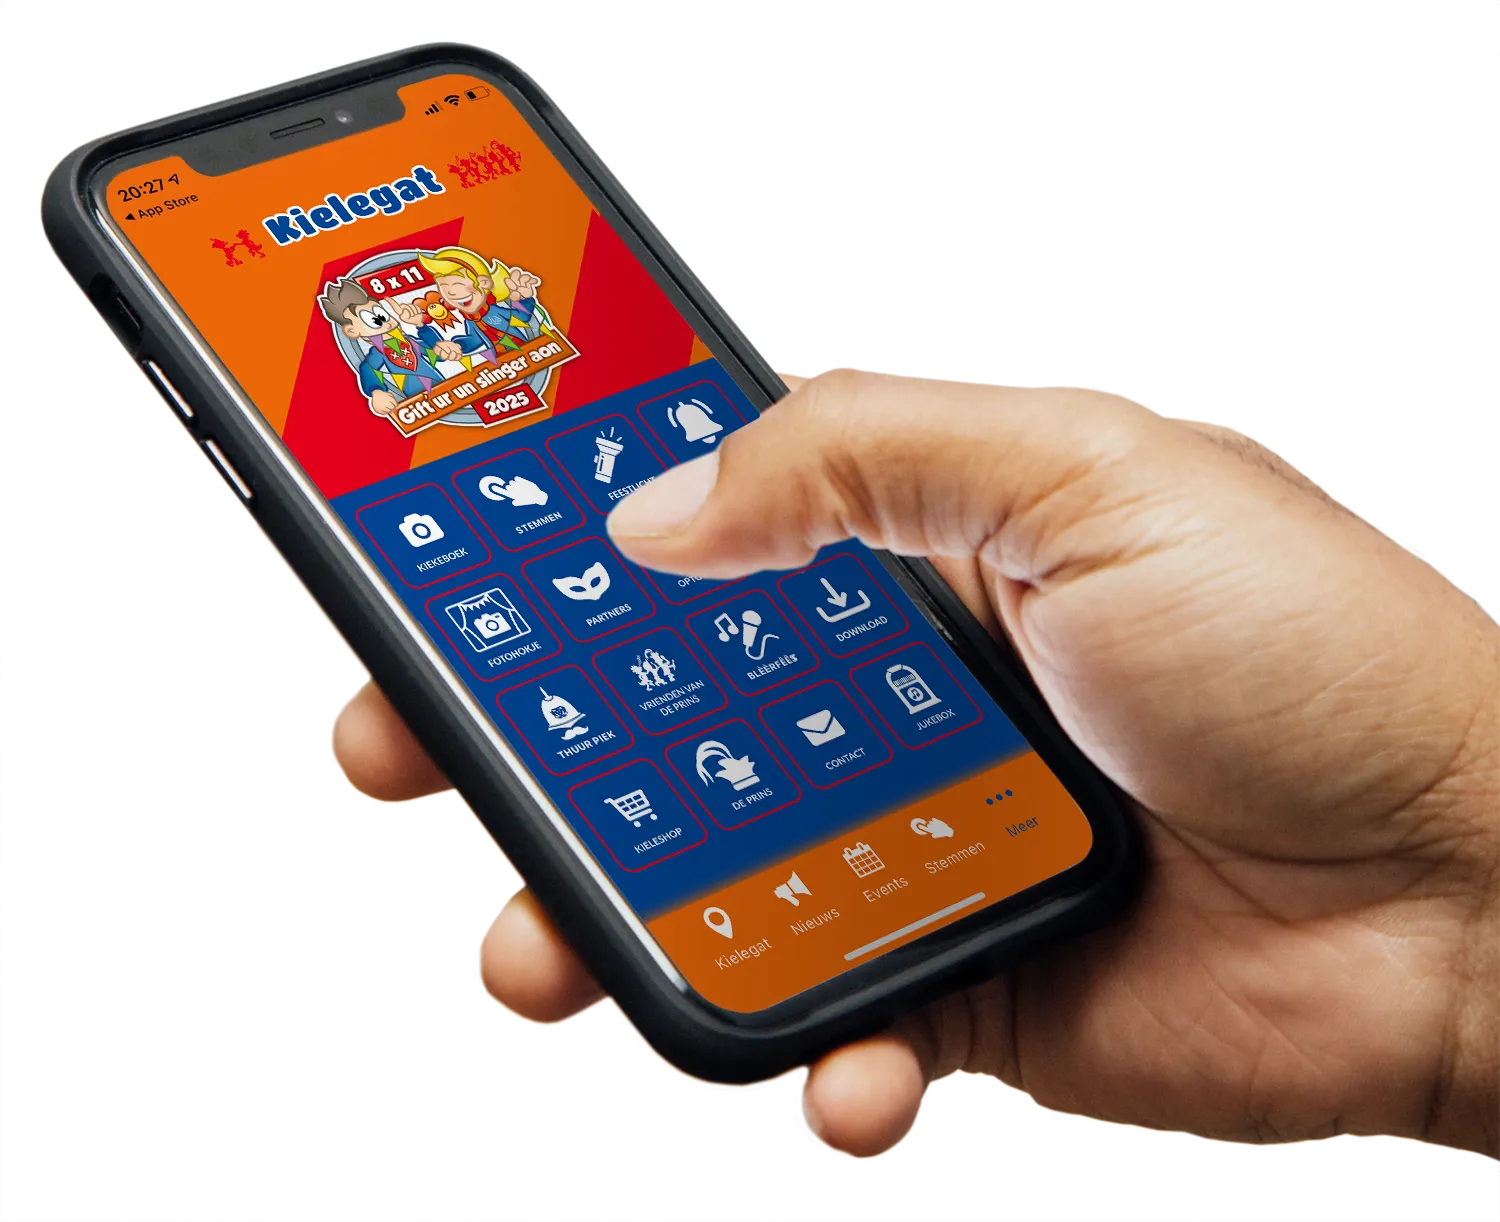
For carnival organisations in the Dutch province of Brabant we built an app platform: one Flutter codebase released as a separate app per organisation, with an admin portal in which the organisation manages news, events, maps and notifications itself. Together the apps have 35,000 active users and simply have to work during carnival, under peak load.
35,000
Active users (2026 season)
7
Apps from one codebase
6
Admin portals in production
Almost 2 million
Screen views in one season
Read the case
MG Devs
Why a small senior team
In AI, data and backends the value is in the decisions. You want those made by the people who also write the code.
01
You talk to the builders
The engineer you speak to also designs and builds your system. There is no account manager in between.
02
Every change is demonstrably tested
Each change goes through a pull request, automated checks and a preview environment. Nothing goes live without human approval.
03
Security and privacy from day one
AI processing inside the EU, personal data masked and access only after sign-in. That is fixed in the design before we build.
04
Live systems keep working
We maintain apps whose users never update. That is why we change data and APIs in a backwards-compatible way, always.
Specialist in Java and Kotlin, cloud architecture and CI/CD. Has built business-critical systems for over ten years, in logistics and ports, mobility, energy and financial services. Designs our backends, data architecture and AI infrastructure.
Can you set up AI so that data stays inside the EU?
Yes. For a European financial services firm we built a private AI platform in which prompts and completions only travel through European endpoints. Routing fails closed: if a model has no EU endpoint, the request goes to an EU alternative. If there is none either, it is refused.
Which AI models do you work with?
We are model-agnostic. We put a gateway in front of the models, so you choose the right model per task (fast and cheap for bulk, heavy for analysis), with automatic fallback when a provider goes down. That keeps you from being locked in to one vendor.
How do you secure an AI system?
We treat everything a model reads as untrusted input, give agents only the permissions they need and log every action. The AI services publish no ports to the internet themselves, run on pinned software versions and sit in a separate network. Personal data is masked before a model sees it.
Do you work in existing Java or Kotlin codebases?
Yes. We step into existing JVM systems, for example to build new functionality, migrate Java to Kotlin step by step, or add AI features to an existing backend.
Do you use AI yourselves when developing?
Yes, daily. AI agents do analysis, implementation and review for us. Every change then goes through automated checks, gets a preview environment and is only merged after human approval. Agents cannot merge or deploy on their own.
Who will I be working with?
With the engineers themselves. Kevin Bos and Pascal van Hoof do the design, the build and the communication. There is no account manager in between.
Contact
Book a 30-minute intro call
Describe your question in a few sentences. Kevin or Pascal replies personally.